“A good day for Martin Shkreli,” who may try to pin fraud on former counsel

Feds mulling additional charges as CEO’s former company, Turing, gets sued.

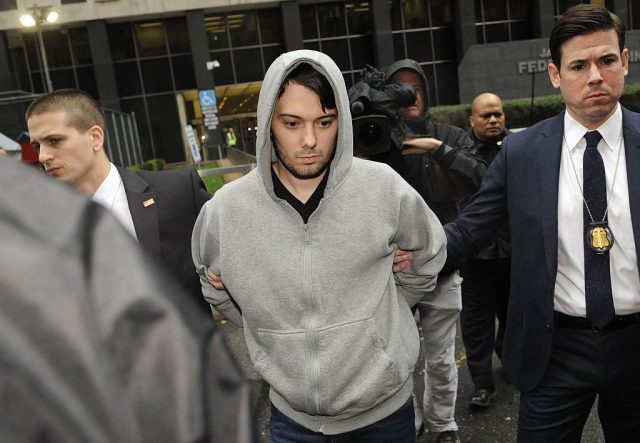
Martin Shkreli, chief executive officer of Turing Pharmaceuticals LLC, exits federal court in New York, US, on Thursday, December 17, 2015. Shkreli was arrested on alleged securities fraud related to Retrophin Inc., a biotech firm he founded in 2011. (credit: Louis Lanzano/Bloomberg via Getty Images)

In a Tuesday court hearing, a federal judge delayed setting a trial date for Martin Shkreli, the disgraced founder and ex-CEO of Turing Pharmaceuticals who was indicted on seven counts of securities fraud charges last December.

Shkreli and his lawyer requested the delay after learning recently that prosecutors are considering filing more charges against the embattled former executive and his ex counsel, Evan Greebel, who was already charged with one count of wire-fraud conspiracy. The new potential charges—along with the initial ones—relate to allegations that the pair ran a Ponzi-like scheme, in which they funneled millions of dollars out of Retrophin, another of Shkreli’s pharmaceutical companies, to cover losses from two hedge funds Shkreli managed.

In the Brooklyn federal court Tuesday, prosecutors told the judge that they would decide if they would file new charges within the month.

Read 5 remaining paragraphs | Comments
HP’s new All-in-One is sleek, borderless, and has a really neat webcam

Smart all-in-ones and attractive laptops are the highlights of HP’s spring collection.

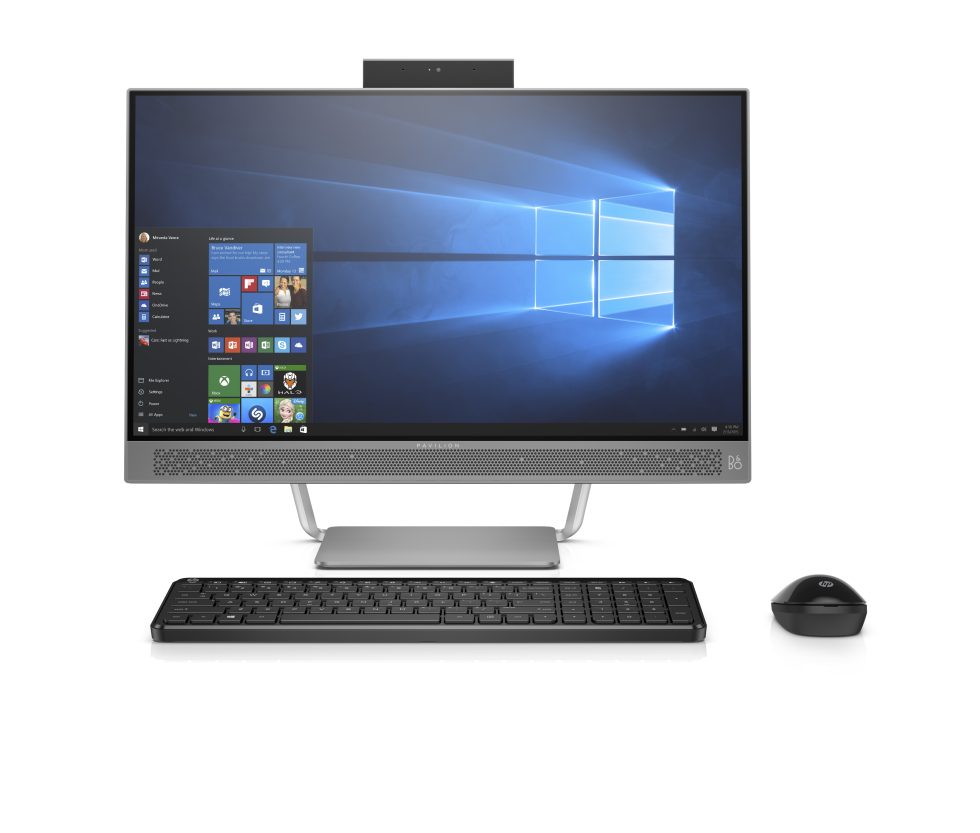
Push down on the rectangle at the top and it retracts inside the system, disconnecting the webcam and microphone. (credit: HP)


HP has been impressing us lately with some of its system design—the new Spectre laptop is particularly eye-catching. A new all-in-one desktop announced today is similarly striking. The name is a little ungainly—the HP Pavilion All-in-One with Micro-Edge Display—but while not rolling off the tongue, it sure is descriptive. The 23.8-inch non-touch IPS display has a narrow bezel of just 6.4 mm, bringing the same kind of slimline look that we've been fans of since the Dell XPS 13 came onto the scene.

In the flesh, the machine is extremely good looking, and the narrow bezels make it really stand out. It's a system that'll look good both at home or in the office, with the narrow bezel almost imperceptible.

With prices starting at $749.99, the Pavilion offers a range of Intel Skylake processors, and optional Nvidia GT 930A graphics. This isn't going to be the fastest system ever built, but it should be more than able to handle most things that people throw at it, even light gaming at its native 1920×1080 resolution should be within reach. It can be equipped with up to 16GB RAM and 1TB hybrid disk. Connectivity includes USB Type-C, traditional USB 3.0, Ethernet, 802.11ac Wi-Fi, and HDMI out.

Read 4 remaining paragraphs | Comments

Nintendo stops selling indie game in an attempt to cut off 3DS hackers

Gravity-bending VVVVVV is unavailable after a new exploit is published.

Nintendo has taken popular indie gravity-flipping platform game VVVVVV down from the 3DS eShop after hackers revealed the game can be used to help load unsigned code onto the system. On Sunday, a hacker going by the handle ShinyQuagsire published the newly revealed hacking method, which uses a modified save game to allow the system to load unsigned homebrew software.

The new hack is a bit redundant, since it requires first using an existing 3DS exploit (such as Ninjhax) to load the modified save file onto the 3DS' SD card in the first place. That distinction doesn't seem important to Nintendo, which took the game down from the North American 3DS eShop within a day of the hack's publication (though it is currently still available in the European eShop.

Creator Terry Cavanaugh expressed surprise at the existence of the hacking method on Twitter and said that the need to stack the exploit on top of another hack would "hopefully [mean] I won't need to patch anything, woo." But the game will likely need to see some sort of modification before Nintendo agrees to let it back on the eShop.

Read 2 remaining paragraphs | Comments

Adblock Plus will help users pay publishers and keep a cut for itself

With Flattr Plus, users set a monthly budget to pay for content around the Web.

(credit: Dave)

The war of words between online publishers and makers of ad-blocking software has heated up in recent years. Now, a maker of popular ad-blocking software has a new project it says will help online publishers get paid.

Adblock Plus has joined up with Flattr to create "Flattr Plus," a system for Web users who want to pay online content creators. Flattr Plus users will set their own monthly budget that will pay favorite bloggers, musicians, artists, or newspapers. The payments will be apportioned automatically, based on a user's engagement with various websites.

Flattr was co-founded by a man who already knows a thing or two about running controversial Web services: Peter Sunde, who also created and operated The Pirate Bay.

Read 6 remaining paragraphs | Comments

Huge number of sites imperiled by critical image-processing vulnerability [Updated]

Attack code exploiting critical ImageMagick vulnerability expected within hours.

(credit: Tim Green)

A large number of websites are vulnerable to a simple attack that allows hackers to execute malicious code hidden inside booby-trapped images.

The vulnerability resides in ImageMagick, a widely used image-processing library that's supported by PHP, Ruby, NodeJS, Python, and about a dozen other languages. Many social media and blogging sites, as well as a large number of content management systems, directly or indirectly rely on ImageMagick-based processing so they can resize images uploaded by end users.

According to developer and security researcher Ryan Huber, ImageMagick suffers from a vulnerability that allows malformed images to force a Web server to execute code of an attacker's choosing. Websites that use ImageMagick and allow users to upload images are at risk of attacks that could completely compromise their security.

Read 9 remaining paragraphs | Comments

Verizon workers’ union wants investigation of forced fiber upgrades

Verizon calls complaint “ridiculous,” just a negotiating tactic during strike.

(credit: Virginia Tech)

A union representing Verizon workers has asked the Federal Communications Commission to investigate the company’s copper-to-fiber upgrades, saying Verizon is pressuring customers to switch even when they don’t want to.

The complaint stems from Verizon’s “Fiber is the Only Fix” program, in which Verizon automatically sets up copper-to-fiber upgrades when customers with copper-based landline phones call for repairs twice in 18 months. Though many customers welcome the shift to fiber because it brings more reliable and faster Internet access, some prefer to keep copper-based landline phones because they can remain in service during long power outages.

The union, the Communications Workers of America (CWA), claims Verizon is violating a ban on deceiving consumers and a requirement that customers be given 90 days' notice before retiring copper networks.

Read 17 remaining paragraphs | Comments

VATM: Vectoring in Mecklenburg-Vorpommern braucht 20.476 KVz

In einem dünn besiedelten Flächenland wie Mecklenburg-Vorpommern ist der Vectoring-Ausbau nicht einfach. Das exklusive Vectoring-Angebot der Deutschen Telekom halte nicht, was es verspricht, meint der Branchenverband VATM. (Vectoring, Telekom)

In einem dünn besiedelten Flächenland wie Mecklenburg-Vorpommern ist der Vectoring-Ausbau nicht einfach. Das exklusive Vectoring-Angebot der Deutschen Telekom halte nicht, was es verspricht, meint der Branchenverband VATM. (Vectoring, Telekom)

Clearly your Raspberry Pi needs a tube amp (crowdfunding)

Clearly your Raspberry Pi needs a tube amp (crowdfunding)

The Raspberry Pi line of devices are inexpensive, low-power, credit card-sized computers. But while there are USB ports for connecting a keyboard, mouse, gamepad, or other accessories, there are also a series of GPIO (General Purpose Input/Output) pins that allow you to connect hardware in other ways.

For instance, you can connect a HAT (Hardware Attached on Top) board to add motor controllers, GPS, a display, or other features.

Now the folks at Pi 2 Design has launched a Kickstarter campaign for one of the most ridiculous/awesome-looking HATs I’ve seen.

Continue reading Clearly your Raspberry Pi needs a tube amp (crowdfunding) at Liliputing.

Brazilian judge blocks WhatsApp for 72 hours, but it still works over VPN, Wi-Fi

“This decision punishes more than 100 million Brazilians who rely on our services.”

(credit: samazgor)

A Brazilian judge has ordered (Google Translate) that all mobile phone providers in the country block WhatsApp traffic for 72 hours, beginning yesterday.

However, Brazilians are discovering that the ban only covers mobile carriers—so Brazilians still can use WhatsApp over Wi-Fi or a VPN connection over their mobile data plan.

Judge Marcel Maia Montalvão issued the order Monday while working on an ongoing drug case that remains under seal. This was the same judge who ordered that Facebook executive Diego Dzodan should be arrested in March after "repeated non-compliance with court orders." Dzodan was released soon after.

Read 5 remaining paragraphs | Comments

Aging and bloated OpenSSL is purged of 2 high-severity bugs

Padding oracles and memory corruption threats caused by use of older schemes.

(credit: Ben Schumin)

Maintainers of the OpenSSL cryptographic library have patched high-severity holes that could make it possible for attackers to decrypt login credentials or execute malicious code on Web servers.

The updates were released Tuesday morning for both versions 1.0.1 and 1.0.2 of OpenSSL, which a large portion of the Internet relies on to cryptographically protect sensitive Web and e-mail traffic using the transport layer security protocol. OpenSSL advisories labeled the severity of both vulnerabilities "high," meaning the updates fixing them should be installed as soon as possible. The fixes bring the latest supported versions to 1.0.1t and 1.0.2h.

The decryption vulnerability is the result of what cryptographers call a padding oracle weakness, which allows attackers to repeatedly probe an encrypted payload for clues about the plaintext content inside. According to TLS expert Filippo Valsorda, the bug allows for only 16 bytes of encrypted traffic to be recovered, and even then only when an end user sends it repeatedly. Still, the conditions might make it possible for an attacker with the ability to monitor the connection to obtain authentication cookies and other small chunks of encrypted text, Valsorda wrote. The vulnerability is indexed as CVE-2016-2107.

Read 3 remaining paragraphs | Comments